Scalable Multi-Tenant Authentication & RBAC Workflows in Healthcare SaaS
Designing hardened JSON Web Token authentication, refresh token rotation, tenant isolation, and granular role hierarchies.
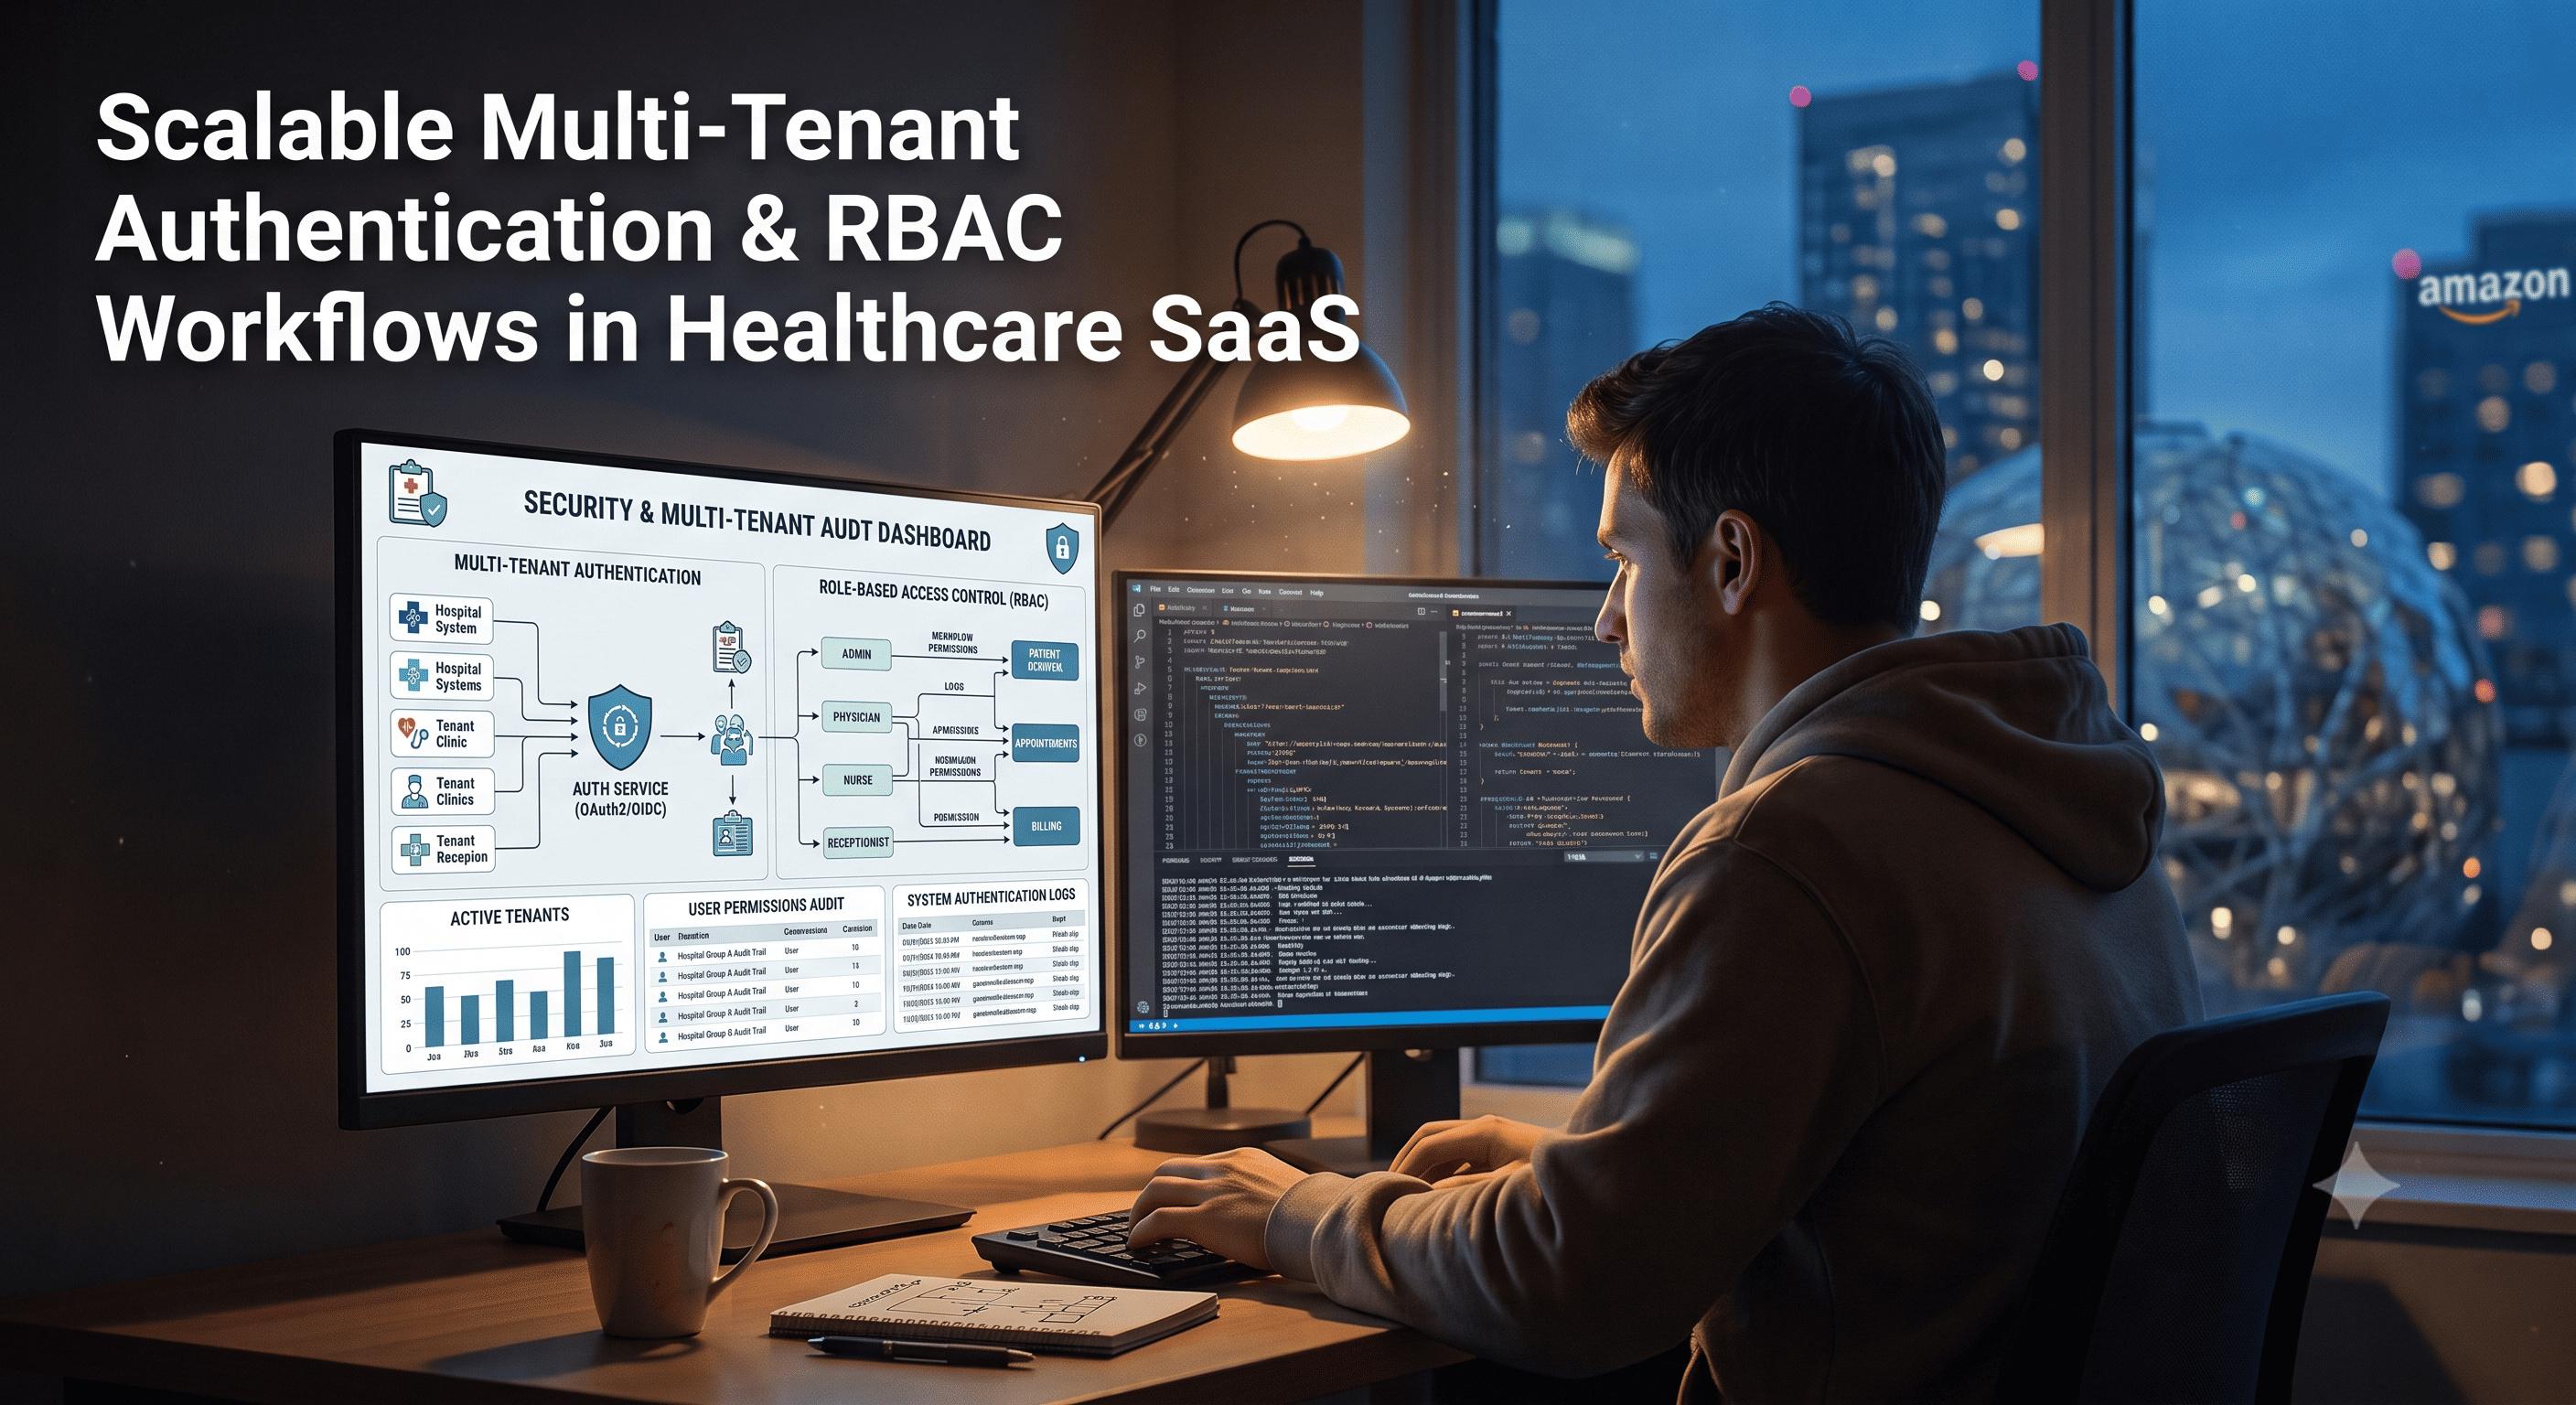
Healthcare software requires rigorous security, tenant isolation, and tamper-proof access controls.
1. Dual-Token Architecture with Rotation
Use short-lived JWT access tokens (15-minute validity) paired with cryptographically random refresh tokens stored in HTTP-only, secure, same-site cookies.
2. Strict Tenant Isolation
Every database query enforces a mandatory tenant filter (hospitalId) through middleware context injection, preventing data leakage across institutions.
3. Hierarchical Permission Trees
Implement bitmask or policy-based authorization where consultant roles inherit read permissions but require elevated approval for prescription modifications.
Rahul
SDE & Team Lead specializing in scalable Node.js microservices, distributed systems, and rapid startup MVP delivery.
More Articles
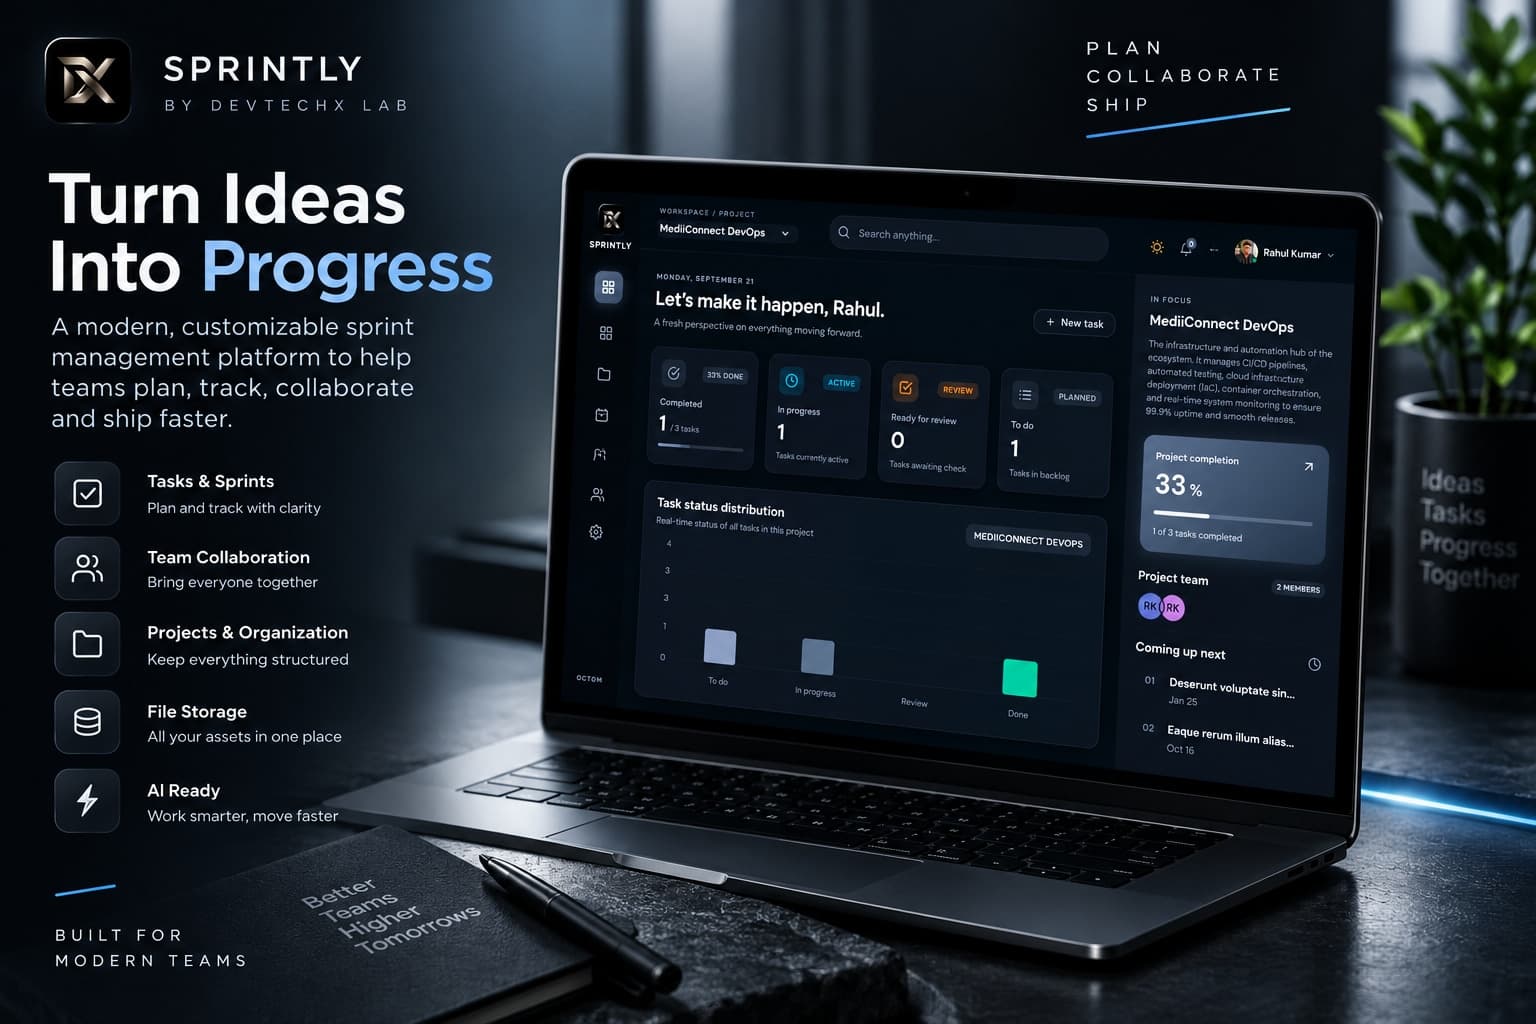
Building Sprintly: Background Workers, 2FA, Notifications & Cost-Efficient SaaS Deployment
A deep engineering case study of building Sprintly, covering independent background workers, web notifications, TOTP security, task management, Docker, and cost-efficient deployment with Render and Vercel.
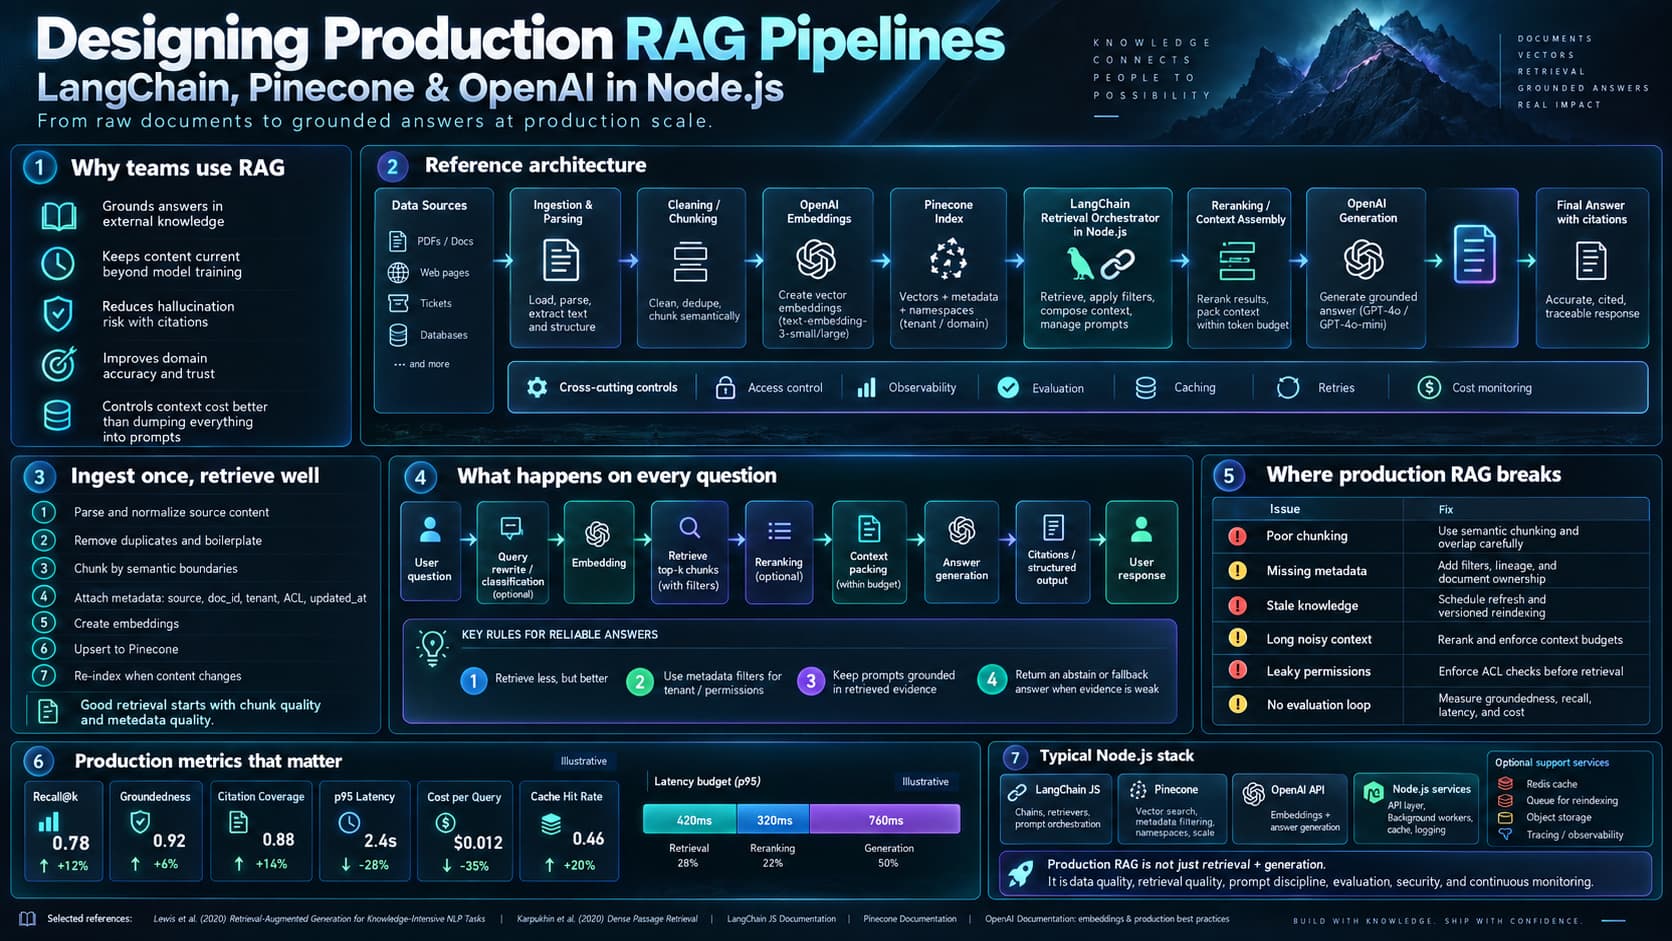
Designing Production RAG Pipelines with LangChain, Pinecone & OpenAI in Node.js
A complete guide to building low-latency, contextual Retrieval-Augmented Generation workflows in Node.js and TypeScript.
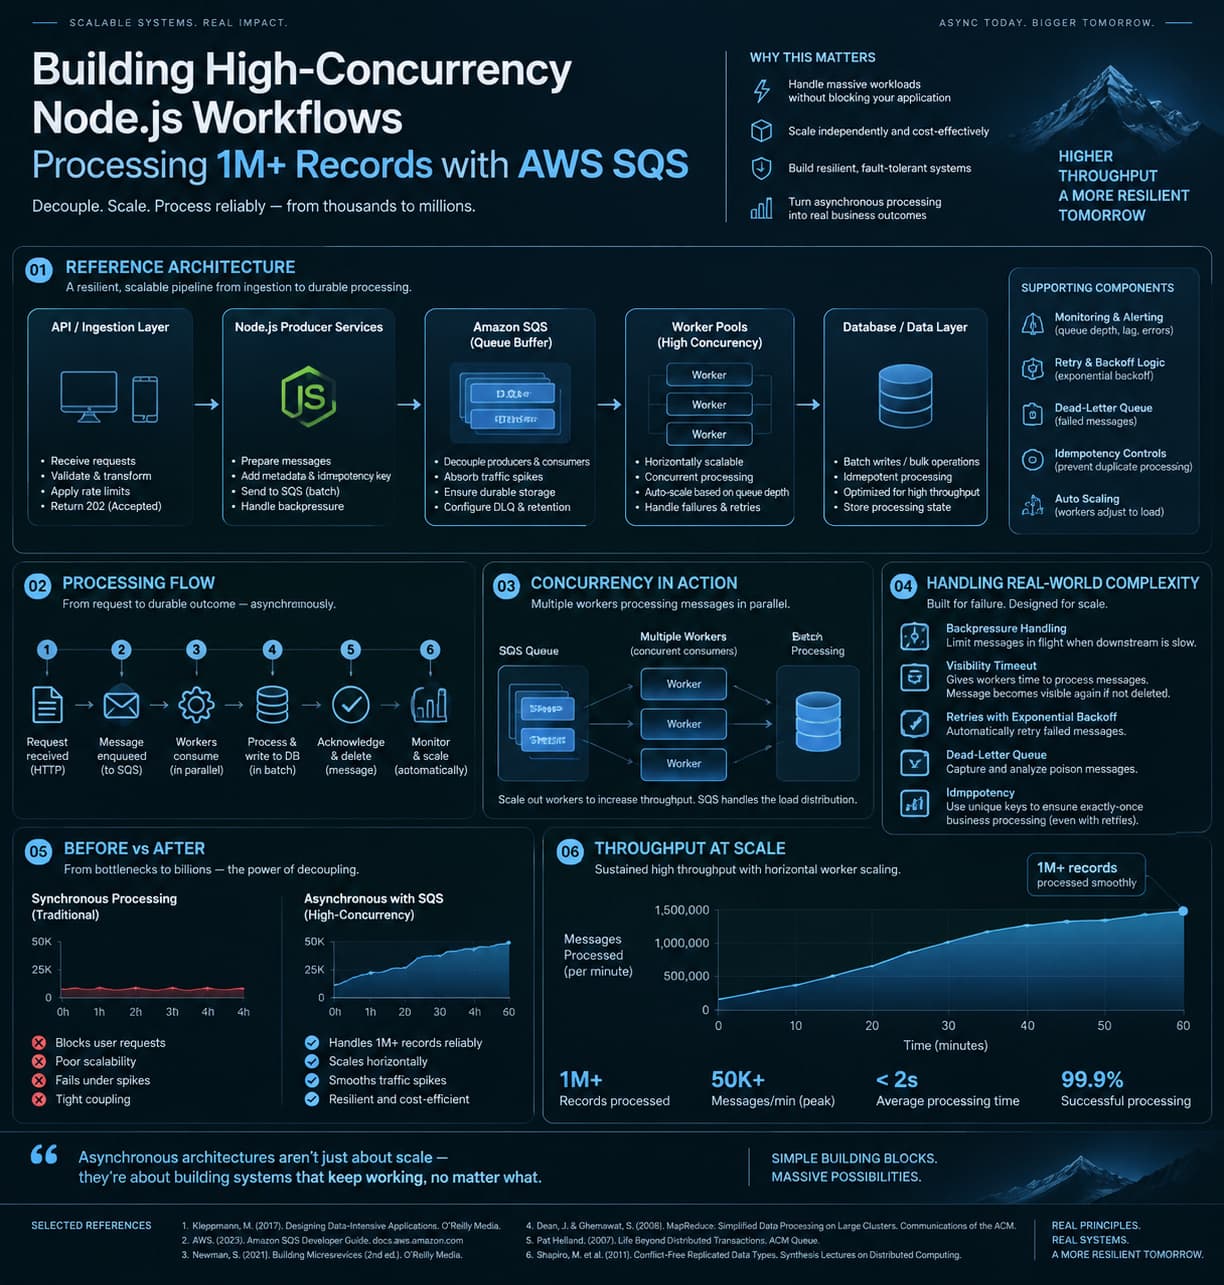
Building High-Concurrency Node.js Workflows Processing 1M+ Records with AWS SQS
Architectural patterns for scaling asynchronous Node.js data pipelines, event-driven queues with AWS SQS, and preventing memory leaks under high throughput.